· Moshe
SBOMs in the Age of AI
Explore how SBOMs must evolve to address the challenges of AI-native software, focusing on data provenance, model lineage, and operational visibility for better governance.
Blog
Releases, research and field notes on securing AI agents, Linux fleets and the software supply chain.
· Moshe
Explore how SBOMs must evolve to address the challenges of AI-native software, focusing on data provenance, model lineage, and operational visibility for better governance.
· Codenotary Team
The U.S. government's suspension of Anthropic's Mythos 5 and Fable 5 raises vital concerns about cybersecurity, national security, and the need for better AI governance.
· Dennis
Explore the operational risks of AI systems and how AgentMon enhances security through real-time monitoring and policy enforcement for safer AI interactions.
· Dennis
AI agent cost monitoring with AgentMon: burn rate, oversized prompts, model routing, chargeback. Track LLM spend before it spirals into a finance incident.
· Dennis
Traditional APM misses what's unique to AI agents, reasoning chains, backtracks, tool errors. AI agent performance monitoring with AgentMon, done right.
· Dennis
Prompt injection, secret leaks, dangerous commands, MCP sprawl, five AI agent security risks and how AgentMon catches each one before production.
· Dennis
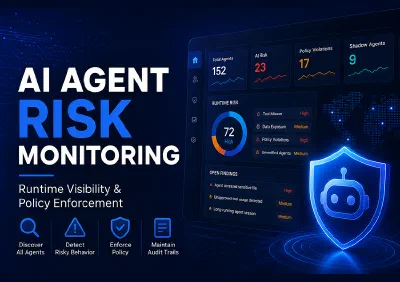
AI agent risk monitoring with AgentMon: score every agent's posture, surface shadow AI, and audit risky actions across your fleet from one Command Center.
· Codenotary Team
Discover how the FS-ISAC advisory highlights the architectural mismatch between legacy vulnerability management and modern cyber threats, emphasizing real-time asset management.
· Dennis
We trained a Deep Q-Network to clear Level 14 of space invaders, a game 50x harder than the original. Here's how the same AI pipeline drives vulnerability detection, security remediation, and CVE threat modeling in production.
· Codenotary Team
AI is revolutionizing cybersecurity by automating exploit generation and vulnerability management, shifting the balance between attackers and defenders.
· Codenotary Team
Explore how fragmentation in Linux security tools hinders effective protection and discover a unified approach for proactive security operations.
· Codenotary Team
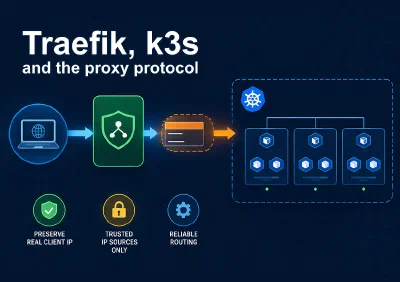
Learn how to configure Traefik with k3s to maintain the original client IP using the proxy protocol, enhancing security and traffic management in your Kubernetes cluster.
We use Google Analytics cookies to understand how the site is used. Nothing is loaded unless you accept. Privacy policy